

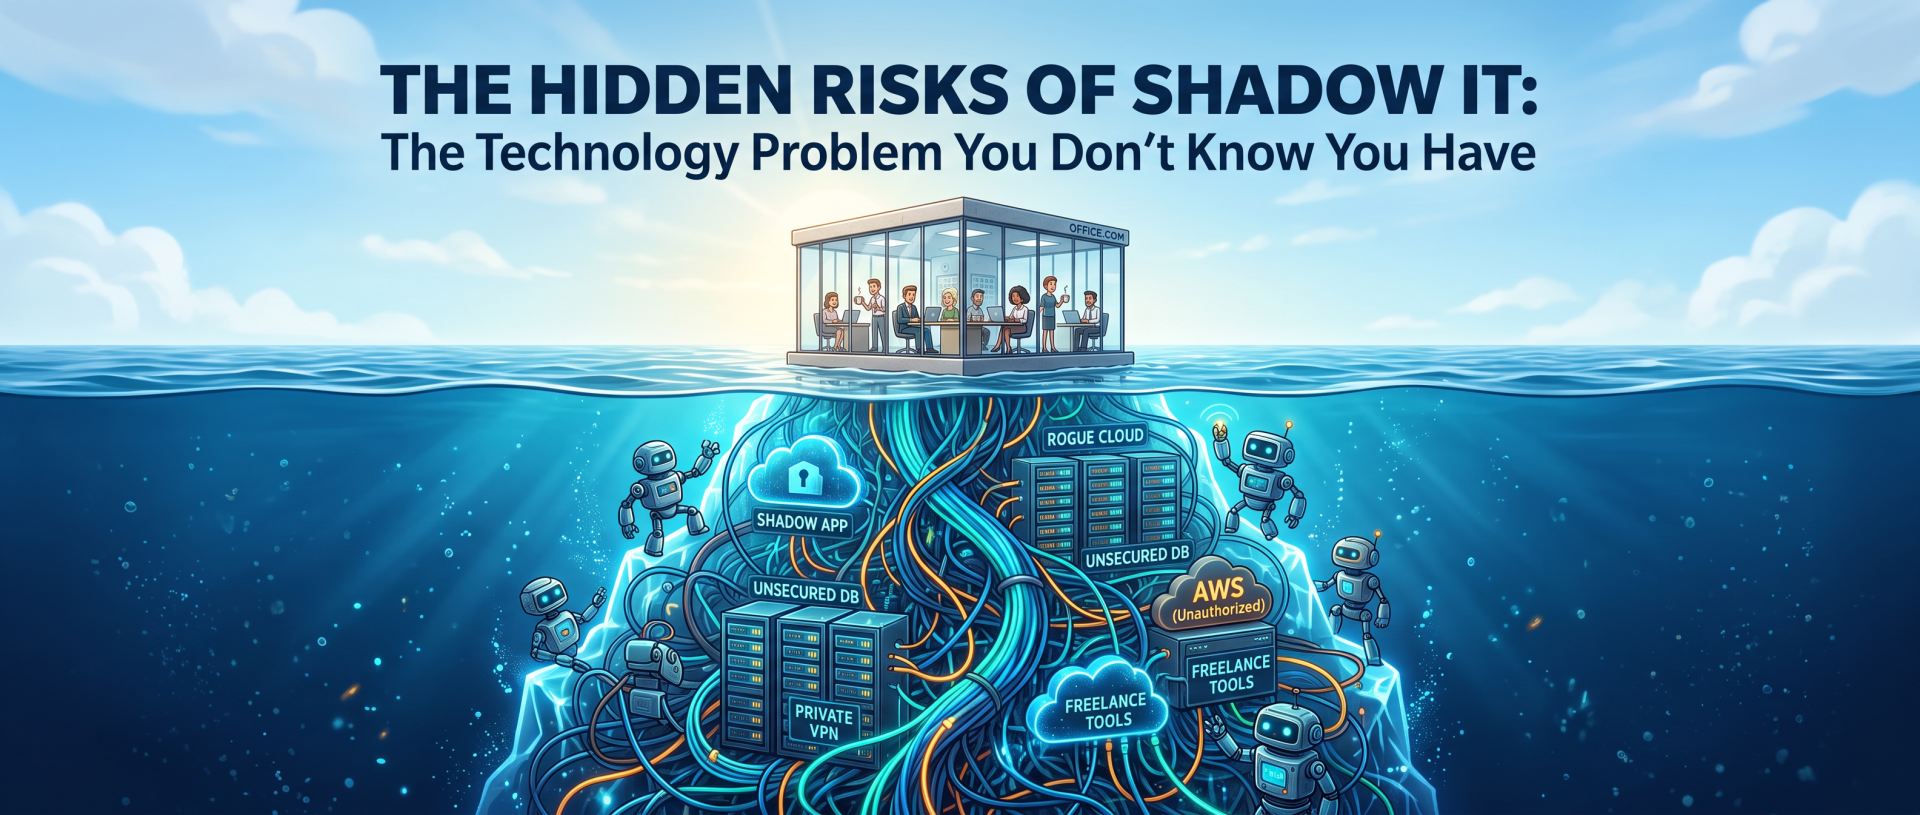
The Technology Problem You Don’t Know You Have
Walk into almost any modern office and you’ll find it.
Not the coffee machine everyone complains about. Not the printer that mysteriously jams only when executives need something printed.
Something far more common and potentially far more dangerous.
A salesperson using a personal Dropbox account to share large files. A marketing team collaborating through a free project management app that IT has never approved. An employee uploading company data into an AI tool because it helps them finish tasks faster.
Welcome to the world of Shadow IT.
Most organizations have it. Many don’t realize how much of it exists. And almost all underestimate the risks it creates.
The irony is that Shadow IT usually doesn’t begin with bad intentions. It begins with good employees trying to get work done. Unfortunately, good intentions don’t stop security breaches.
What Exactly Is Shadow IT?
Shadow IT refers to any software, hardware, cloud service, application, or technology used within an organization without the knowledge, approval, or oversight of the IT department. The term sounds dramatic, like a secret underground network of rogue employees operating from hidden basements. In reality, it’s usually much more ordinary.
An employee signs up for a free file-sharing service because attachments are too large for email.
A team starts using a messaging platform because they prefer it over approved tools.
Someone installs browser extensions or productivity apps without thinking twice.
A department purchases cloud software with a company credit card instead of going through procurement.
None of these actions feel particularly dangerous. That’s what makes Shadow IT so common.
Employees generally aren’t trying to break rules. They’re solving problems.
The challenge is that every unauthorized solution introduces risks that nobody is managing.
Why Shadow IT Is Growing Faster Than Ever
Twenty years ago, Shadow IT was relatively limited. Installing enterprise software often required servers, capital budgets, and IT involvement.
Today, anyone with a browser and a credit card can deploy powerful business tools in minutes.
Cloud computing has removed many traditional barriers. Software-as-a-Service (SaaS) platforms make adoption incredibly easy. Artificial intelligence tools can be accessed instantly. Employees no longer need permission to experiment with technology.
The rise of remote and hybrid work has accelerated the trend even further.
When people work from multiple locations, they naturally search for tools that help them communicate, collaborate, and stay productive. If approved systems feel slow or restrictive, employees often find alternatives.
It’s human nature.
When work needs to get done, convenience usually wins.
The Security Risks Hiding Beneath the Surface
The most obvious concern with Shadow IT is cybersecurity.
Every unapproved application becomes another potential entry point into the organization’s environment.
Imagine locking every door in your house, installing security cameras, and setting up an alarm system, only to discover someone left a window open in the basement. That open window represents Shadow IT.
IT teams cannot secure what they cannot see.
An unauthorized cloud storage platform may contain sensitive client files. A free team collaboration app could store internal discussions. An AI tool might receive proprietary business information through user prompts.
Without oversight, organizations lose visibility into:
- Who has access to sensitive data
- Where company information is stored
- How data is protected
- Whether information is being shared externally
- What happens when employees leave
Cybercriminals don’t care whether an application is officially approved. If it contains valuable data, it’s a target.
In many cases, attackers specifically look for less-protected systems because they are easier to compromise.
The Compliance Nightmare Nobody Wants
Security concerns are serious. Compliance issues can be even worse.
Many industries must comply with regulations governing how data is collected, stored, processed, and protected.
Healthcare organizations deal with patient privacy requirements. Financial institutions face strict oversight. Businesses handling customer information often must comply with multiple privacy laws and regulations.
When employees use unauthorized applications, compliance controls frequently disappear.
Data may be stored in regions that violate organizational requirements. Records retention policies may not apply. Auditing capabilities might not exist.
Consider a simple example.
An employee exports customer information into a personal productivity tool to create reports faster.
The task seems harmless.
However, if that data is now stored outside approved systems, the organization may no longer have control over how it’s protected, retained, or deleted.
What began as a shortcut can quickly become a compliance incident.
The Hidden Financial Costs
Organizations often focus on security risks while overlooking the financial impact of Shadow IT.
Ironically, tools adopted to save money can end up costing far more.
Unauthorized software purchases create duplicate spending across departments. Multiple teams may pay for similar services without realizing an approved solution already exists.
Subscription fatigue compounds the problem.
Five dollars per month doesn’t sound significant.
Multiply that by dozens of applications, hundreds of employees, and several years, and the number becomes surprisingly large.
Then there are indirect costs:
- Security investigations
- Compliance reviews
- Incident response efforts
- Data migration projects
- Vendor management complexity
- Lost productivity from fragmented workflows
Shadow IT can quietly become one of the most expensive technology issues an organization faces.
The Data Fragmentation Problem
Imagine trying to complete a puzzle when pieces are scattered across ten different rooms.
That’s what happens when organizations lose control of where information resides.
Data becomes fragmented across multiple platforms, applications, and services.
Important files may exist in approved systems, personal cloud storage accounts, collaboration platforms, AI tools, and employee laptops simultaneously.
Soon nobody knows which version is correct.
Teams spend more time searching for information than using it.
When employees leave, institutional knowledge often leaves with them because critical information was stored in systems nobody else knew existed.
The result is confusion, inefficiency, and unnecessary risk.
When AI Becomes Shadow IT
Artificial intelligence has introduced an entirely new dimension to the Shadow IT challenge.
Many employees are experimenting with AI tools to improve productivity. In most cases, they are simply trying to work smarter.
The issue arises when confidential business information is entered into external AI platforms without understanding how that information is processed, retained, or used.
Employees may upload:
- Client data
- Financial information
- Internal reports
- Source code
- Strategic plans
- Proprietary intellectual property
Without proper governance, organizations may unintentionally expose sensitive information through well-intentioned AI use.
This doesn’t mean organizations should avoid AI.
It means they need clear policies, approved platforms, employee training, and visibility into how AI tools are being used.
Why Banning Shadow IT Rarely Works
Many organizations respond by attempting to prohibit everything.
The logic seems reasonable:
“No unauthorized technology. Problem solved.”
Reality is more complicated.
Employees adopt Shadow IT because they are trying to overcome obstacles. If approved tools cannot meet business needs, restrictions alone will simply encourage users to find more creative workarounds.
Successful organizations focus on understanding why Shadow IT exists.
They ask:
- What problems are employees trying to solve?
- Which approved tools are creating friction?
- Where are business needs going unmet?
- How can technology governance become easier rather than harder?
When IT becomes a business enabler instead of a gatekeeper, employees are far more likely to seek approval before adopting new tools.
Building a Smarter Strategy
The goal isn’t eliminating every instance of Shadow IT.
That would be nearly impossible.
Instead, organizations should focus on visibility, governance, and collaboration.
Effective strategies include:
- Conducting regular technology audits
- Monitoring SaaS and cloud application usage
- Establishing clear approval processes
- Providing secure alternatives employees actually want to use
- Creating practical AI governance policies
- Educating employees about security and compliance risks
- Encouraging open communication between departments and IT
The organizations that manage Shadow IT effectively don’t rely solely on technology controls.
They build a culture where people understand both the risks and the reasons behind security requirements.
How MSPs Like Ethixa Solutions Can Help
Many businesses lack the time, resources, or visibility needed to understand the full extent of Shadow IT across their environments.
Managed Service Providers (MSPs) can help organizations gain insight into technology usage, improve governance processes, strengthen security controls, and identify potential compliance concerns. They can also assist with cloud management, security monitoring, user education, and AI governance initiatives.
Most importantly, MSPs help businesses balance productivity with security, ensuring employees can work efficiently without creating unnecessary risk.
Final Thoughts
Shadow IT isn’t really a technology problem.
It’s a people problem, a process problem, and increasingly, a visibility problem.
Employees want to work efficiently. Businesses want to remain secure. Those goals are not in conflict.
The challenge is creating an environment where innovation can thrive without sacrificing security, compliance, or operational control.
The next unauthorized app likely isn’t being installed by a malicious insider plotting corporate destruction.
It’s probably being installed by a hardworking employee trying to make their day easier.
And that’s exactly why Shadow IT deserves attention.
Because the biggest risks are often the ones hiding in plain sight.
Leave a Reply