
·
The Modern Scam Survival Guide for Employees
Learn how to train employees to spot modern phishing, impersonation, BEC, and AI-assisted scams using practical habits that improve security.
·
How to Know If Your Business Has Been Compromised
Cyberattacks rarely begin with a dramatic red screen announcing, “Congratulations, you’ve been hacked.” Real compromises are usually less theatrical. Maybe an employee gets an MFA prompt at 2:17 a.m. Someone notices an email in their Sent folder that they swear they did not send. A vendor calls about a strange invoice. Your server suddenly gets…
·
Your Employees Aren’t the Enemy: Rethinking Human Cyber Risk
Why effective security awareness focuses on behavior and systems instead of finding someone to blame There is a familiar scene in cybersecurity training. An employee receives a simulated phishing email. It looks surprisingly convincing. Maybe it appears to come from a vendor they recognize. Maybe it creates just enough urgency to catch them between a…
·
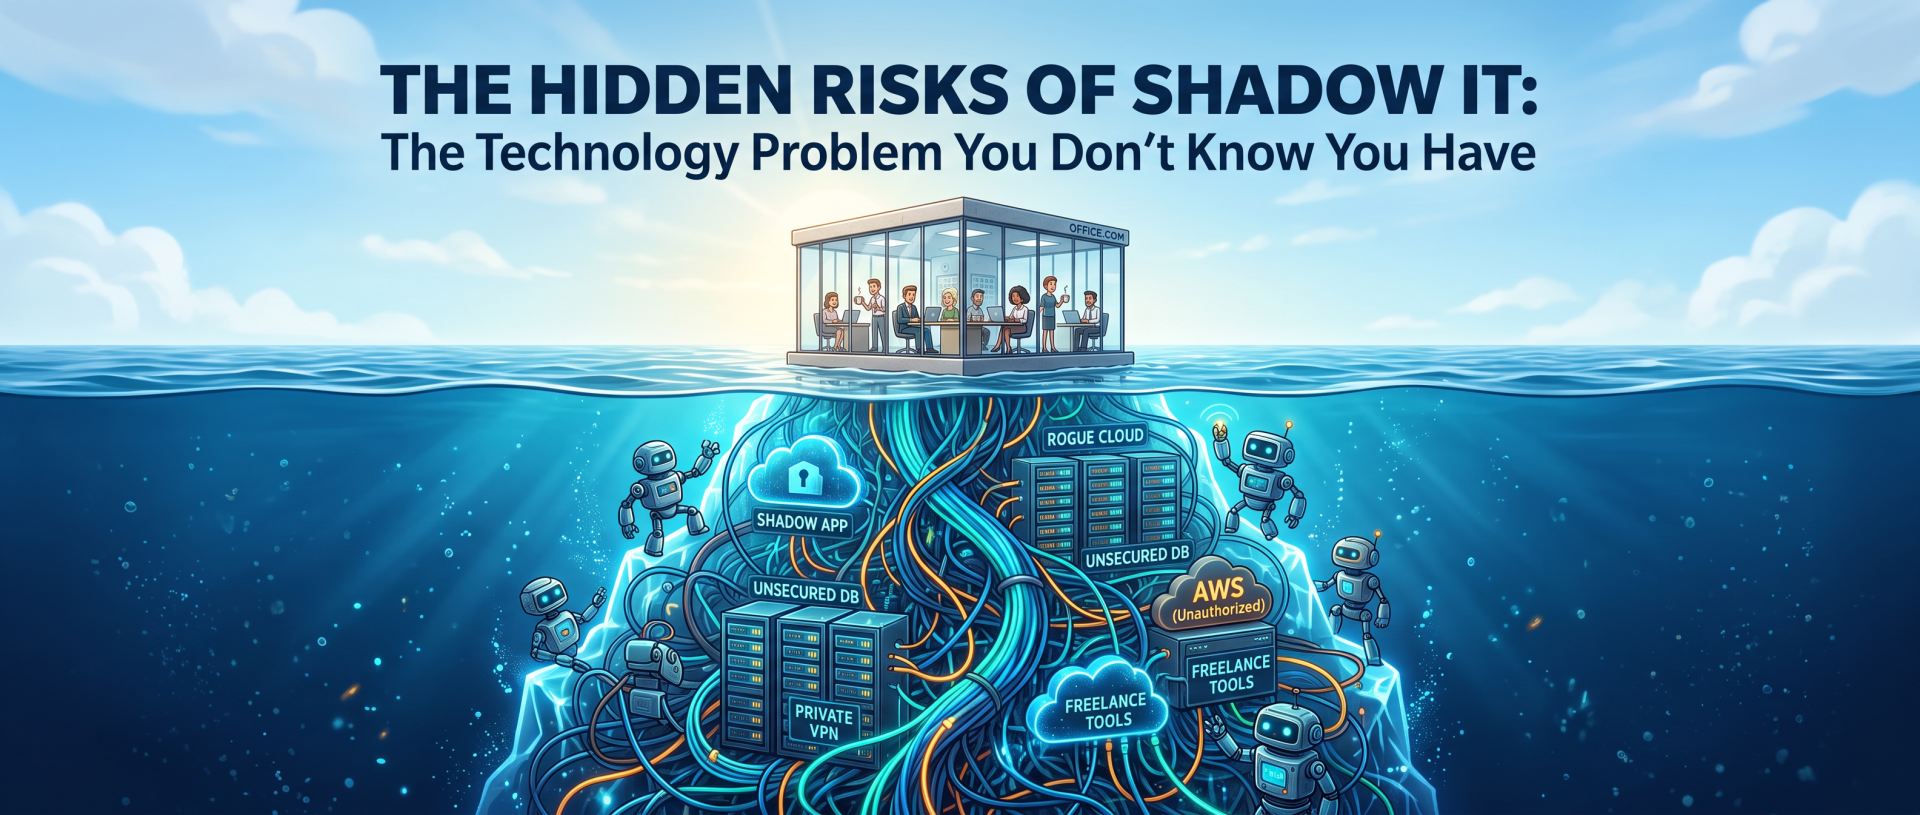
The Hidden Risks of Shadow IT
Shadow IT is growing rapidly across modern businesses. Learn the security, compliance, financial, and AI-related risks of unauthorized technology and how to manage them effectively.

·
Where Your Technology Budget Is Quietly Disappearing
Discover five common sources of technology cost leakage in SMBs and learn how to control hardware, software, network, productivity, and IT management expenses.

·
The Smart Business Guide to Annual IT Budget Planning
Learn how to create an annual IT budget that supports growth, reduces surprises, improves cybersecurity planning, and creates predictable technology spending with help from an MSP.

·
The Risk Behind “Just Google It”
Introduction: A Habit That Became a Vulnerability For most people, using a search engine is second nature. When you need to log into payroll, access your email, or download software, you probably open a browser, type the name of the service, and click the first result you see. It feels efficient. It feels safe. And…

·
Why Zero Trust Security Matters More Than Ever for SMBs
Learn what Zero Trust security is, why it matters, and how SMBs can implement it with help from MSPs like Ethixa Solutions.

·
The Business Case for a Standardized Microsoft Technology Stack
Learn how standardizing Microsoft 365, Azure, and Entra ID reduces cybersecurity, compliance, and operational risk while improving scalability and governance.

·
A Plain‑English Guide to Microsoft Security for Growing Businesses
A clear, business‑friendly guide to Microsoft Security for SMB leaders. Learn the key products, costs, best practices, and why MSPs are essential.